מאמרים / ISO 27001

ב-ISO 27001, נוהל הוא רק תחילת השיחה

הראיות מספרות יותר מהנהלים.

ARTICLES / ISO 27001

For ISO 27001, a policy is only the start of the conversation

The evidence says more than the policies.

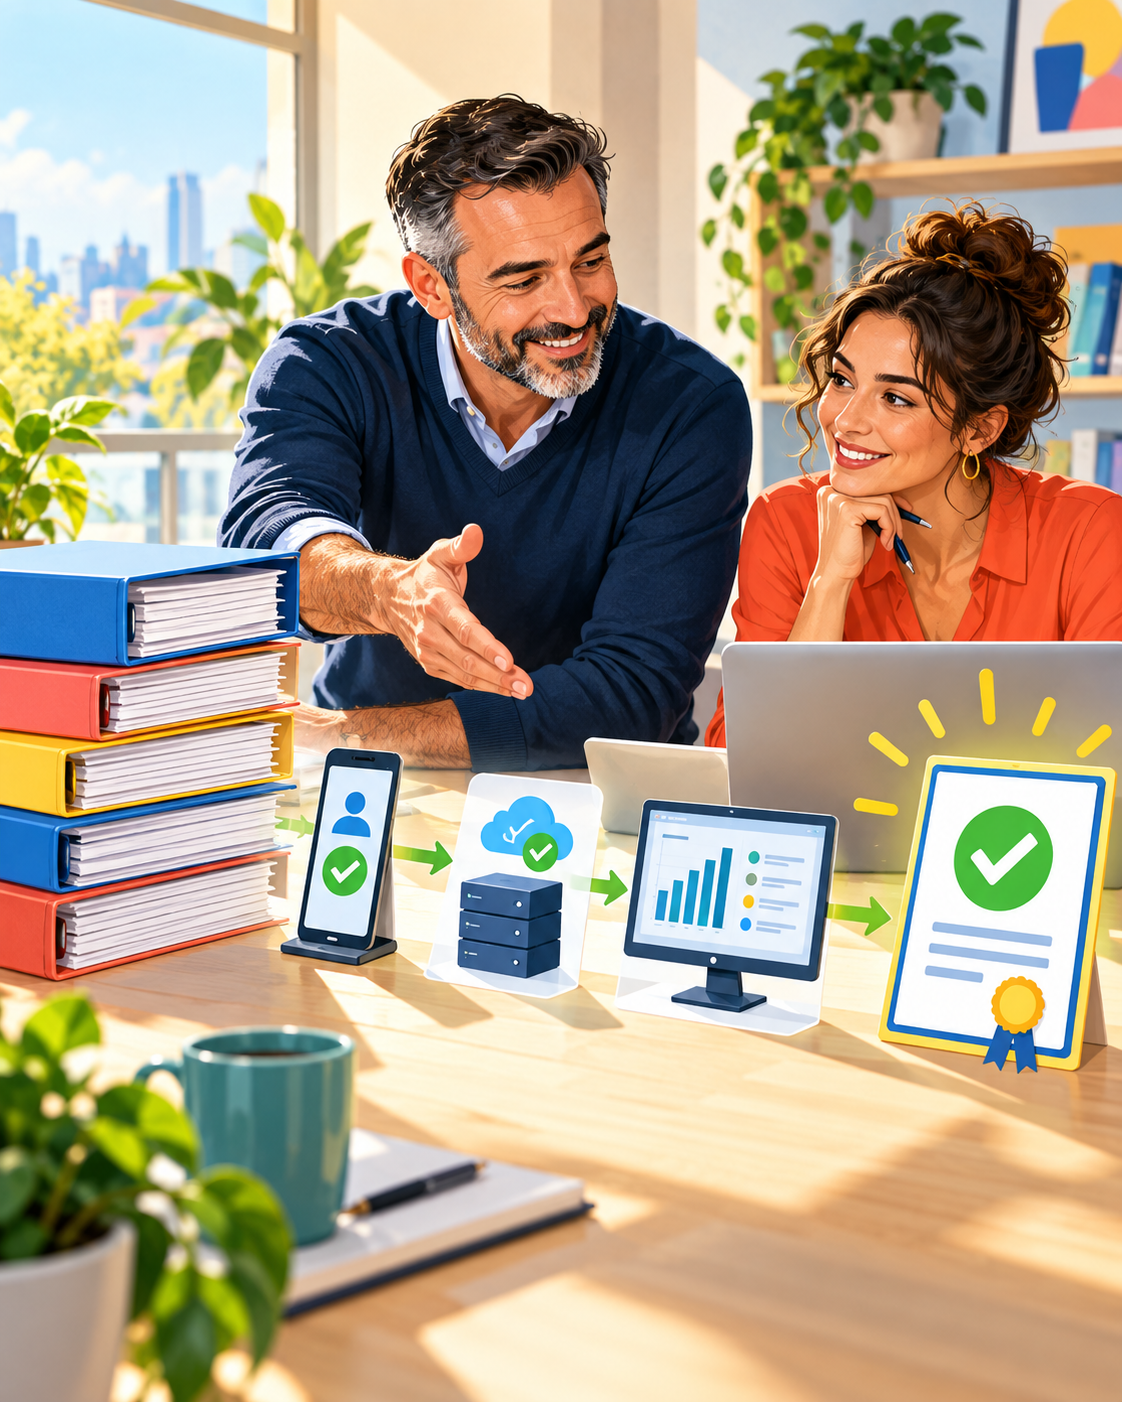
איור צבעוני של צוות הבוחן ראיות אבטחה מעשיות, הרשאות וגיבויים לקראת ביקורת ISO 27001

בביקורת ISO 27001, המשפט "יש לנו נוהל" הוא רק תחילת השיחה.

מה שיותר מעניין אותי הוא מה קרה בפועל.

נוהל אומר שהגישה למערכות נבדקת מדי פעם. מתי בדקתם הרשאות בפעם האחרונה, ומה השתנה בעקבות הבדיקה?

מסמך אומר שהגיבויים נבדקים. מתי שחזרתם משהו באמת, וכמה זמן זה לקח?

כתוב שמדווחים על אירועי אבטחה. מי קיבל את הדיווח האחרון, ומה עשיתם אחריו?

אלה לא שאלות שנועדו לתפוס מישהו. הן עוזרות להבין אם האבטחה חיה בארגון, או רק בתיקייה של הביקורת.

כשמגיעים אליי עם ערימה של נהלים ואני לא רואה תיעוד של החלטות, בדיקות ושיפורים, אני יודע שיש עוד עבודה. לא בהכרח עוד מסמך.

אם אתם מתכוננים ל-ISO 27001, תתחילו מהשגרה: מי עושה מה, איך יודעים שזה נעשה, ומה מתקנים כשזה לא עובד. אחר כך תוודאו שהנהלים מתארים את המציאות הזאת.

תעודה היא יעד נחמד. מערכת שעובדת גם ביום שאחרי הביקורת היא העניין.

עוד על העבודה שלנו: https://artofcyber.co.il/

#אבטחת_מידע #ISO27001 #CISO #ניהול_סיכונים

פורסם במקור בלינקדאין: לפוסט המקורי

Colorful illustration of a team reviewing practical security evidence, access and backups for an ISO 27001 audit

In an ISO 27001 audit, "we have a policy" is only the start of the conversation.

What interests me more is what actually happened.

A policy says access to systems is reviewed from time to time. When did you last review permissions, and what changed because of that review?

A document says backups are tested. When did you actually restore something, and how long did it take?

It says security incidents are reported. Who received the last report, and what did you do afterward?

These questions are not meant to catch anyone out. They help show whether security is alive in the organization or only in an audit folder.

When someone comes to me with a stack of policies but I see no record of decisions, tests, and improvements, I know there is more work to do. Not necessarily another document.

If you are preparing for ISO 27001, start with the routine: who does what, how you know it happened, and what you fix when it does not work. Then make sure the policies describe that reality.

A certificate is a nice goal. A system that works the day after the audit is what matters.
More about our work: https://artofcyber.co.il/

#InformationSecurity #ISO27001 #CISO #RiskManagement

Originally published in Hebrew on LinkedIn: view the original post

רוצים לראות מה באמת עובד בארגון?

Want to see what actually works in your organization?

נדבר על זה ←Let's discuss it →