Does the state really protect the economy from cyberattacks?
Yes. But not instead of your organization.
מאת בוריס פוסטילניק, מייסד Art of Cyberפורסם 24 בספטמבר 2026זמן קריאה: 3 דקות
האם המדינה באמת מגינה על המשק ממתקפות סייבר?
התשובה הקצרה: כן. אבל לא במקום הארגון.
בזמן מלחמה רואים יותר רעש: ניסיונות שיבוש, מחיקה, הדלפות ופעולות השפעה. זה מצטלם טוב ומגיע לכותרות.
בזמן שקט העבודה לא נעצרת. להפך. אז אוספים מודיעין, גונבים הרשאות, נכנסים דרך ספקים ומשאירים גישה ליום שבו יהיה בה צורך.
ראינו את זה מול ישראל. אחרי 7 באוקטובר הפעילות האיראנית התחילה בצורה די אופורטוניסטית, ובהמשך הפכה ממוקדת ומתואמת יותר. חלק מהתקיפות שולבו גם בניסיון להשפיע על התודעה, לא רק לפגוע במערכות.
אז איפה המדינה בתמונה?
מערך הסייבר הלאומי עושה עבודה חשובה: מודיעין, התרעות, סיוע דרך 119, תיאום עם תשתיות קריטיות ובנייה של שכבת הגנה לאומית. זה משמעותי. אבל המדינה לא מתקינה MFA אצלכם, לא סוגרת שרת ישן שפתוח לאינטרנט ולא מתרגלת את ההנהלה שלכם ביום חמישי בערב.
גם התוקפים המדינתיים מחפשים לא פעם את הדרך הקלה. מערכת לא מעודכנת. סיסמה חלשה. ספק עם גישה רחבה מדי.
מבחינתי, ארגון שרוצה להיות מוכן צריך להתחיל בחמישה דברים:
לסגור שירותים שלא חייבים להיות חשופים. להפעיל MFA עמיד לפישינג, קודם כול על חשבונות מנהלים. לטפל מהר בפגיעויות במערכות חיצוניות. לבדוק גיבויים באמת, לא רק לסמן שיש. ולתרגל הנהלה: מי מחליט, למי מדווחים ומה ממשיכים להפעיל.
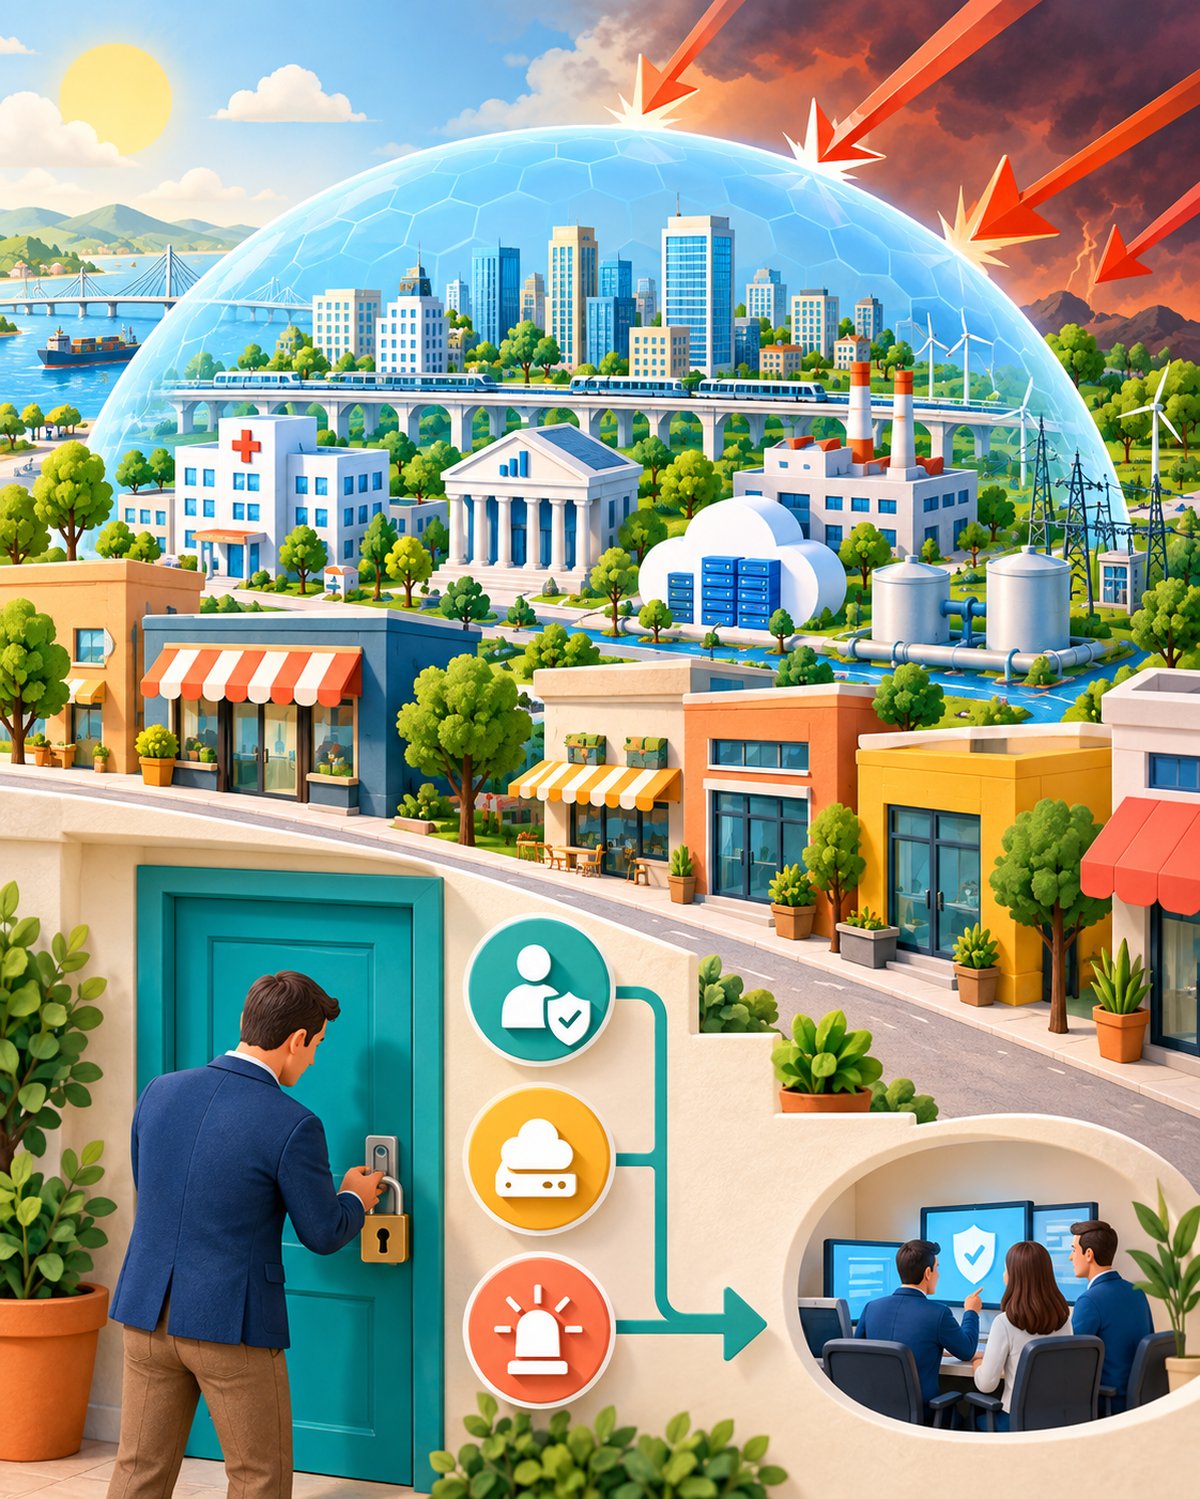
המדינה צריכה להגן על שכבת המאקרו. האחריות על הדלת של הארגון נשארת אצל ההנהלה.
ובסייבר, בזמן מלחמה ובזמן שקט, דלת לא נעולה נשארת דלת לא נעולה.
By Boris Pustilnik, founder of Art of CyberPublished September 24, 20263 min read
Does the state really protect the economy from cyberattacks?
The short answer: yes. But not instead of your organization.
In wartime you see more noise: disruption attempts, wiping, leaks and influence operations. It looks dramatic and makes the headlines.
In quiet times the work does not stop. Quite the opposite. That is when attackers gather intelligence, steal credentials, get in through suppliers and leave access in place for the day they need it.
We saw this against Israel. After October 7, Iranian activity started out fairly opportunistic and later became more targeted and coordinated. Some of the attacks were also combined with attempts to shape public perception, not just to damage systems.
So where does the state fit in?
The Israel National Cyber Directorate does important work: intelligence, alerts, help through the 119 hotline, coordination with critical infrastructure and building a national layer of defense. That matters. But the state will not turn on MFA for you, will not shut down an old server that is exposed to the internet, and will not run a drill with your management team on a Thursday evening.
State-backed attackers also often look for the easy way in. An unpatched system. A weak password. A supplier with too much access.
As I see it, an organization that wants to be ready should start with five things:
Shut down services that do not need to be exposed. Turn on phishing-resistant MFA, starting with admin accounts. Patch vulnerabilities in internet-facing systems quickly. Actually test your backups, do not just tick the box. And drill your management team: who decides, who gets notified and what keeps running.
The state should protect the macro layer. Responsibility for the organization's own door stays with management.
And in cyber, in wartime and in quiet times, an unlocked door is still an unlocked door.